Who: CEOs, product leaders, ops heads, finance and legal teams at enterprises running AI pilots.
What: a July 2026 update to the AI ROI playbook — practical, legally aware steps to turn pilots into measurable profit.
When: July 2026.
Where: global enterprises operating under EU, UK and U.S. oversight (plus U.S. state privacy regimes).
Why it matters: foundation models are standard. The competitive edge is execution: converting model outputs into auditable actions, limiting legal exposure, and tying results to the P&L.
Context: what changed since April–June 2026
Nothing about the core thesis is new: model selection is necessary but not sufficient. What has shifted in the past three months is intensity — commercial and regulatory. Vendors now routinely advertise built‑in logging and drift detection; enterprise procurement asks for “dirty‑data proofs” before contract signature. Regulators continue to push on oversight: the European AI Act’s rules for high‑risk systems are operational realities for firms selling or deploying decisioning tools in the EU, and data protection authorities keep emphasizing DPIAs and purpose limitation under the GDPR. In the U.S., the Federal Trade Commission has reiterated that deceptive automation claims and insufficient oversight can trigger enforcement. At the same time, buyers increasingly report that pilots validated on clean, vendor‑curated data fail in production unless workflows and exception handling are redesigned.
What’s new for July 2026 — practical signals to act on now
- Vendors competing on accountability. Many supply vendors now offer “pilot on your last 90 days” features, built‑in audit trails, and automated drift alerts as standard — if they won’t, treat that as a red flag.
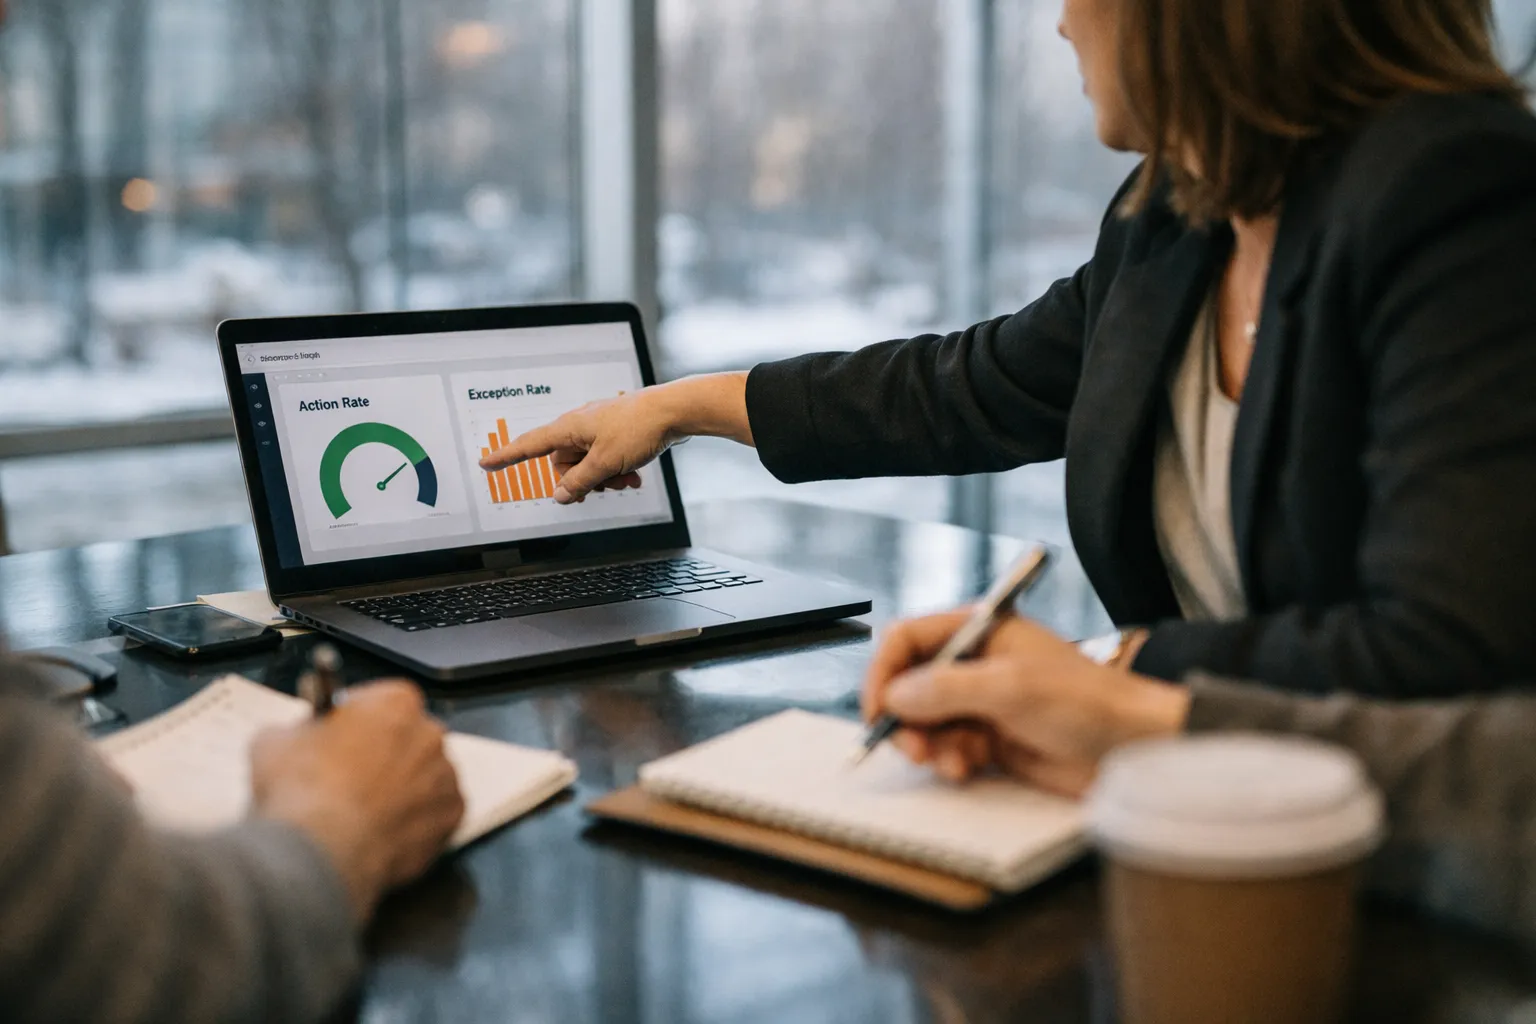
- Boards want compliance + economics. Audit committees and CFOs now demand a one‑page scorecard that combines Action Rate with a compliance flag (DPIA done, logging complete, high‑risk status assessed).
- Regulatory scrutiny is operational. GDPR Article 35 DPIAs, automated decision rules under Article 22 (where applicable), and the EU AI Act’s conformity processes mean legal teams are required at pilot start, not as a late‑stage checklist.
- Exception queues are a liquidity problem. Teams that don’t budget for exception handling see headcount and legal reviews spike; design the queue before you scale.
11 updated truths — short, actionable (July 2026)
1) AI ROI remains a workflow problem — instrument the handoff
Measure whether AI outputs trigger a downstream system change (invoice, CRM update, claim settlement). If the output only helps a human type faster, ROI will be limited. Choose one repeatable workflow and replace a full human step.
2) Stop reporting “hours saved” as the headline KPI
Pick a P&L metric: lower cost per item, increased capacity sold, reduced Days Sales Outstanding (DSO), or avoided chargebacks. Tie the metric to a named owner with budget authority.
3) Action Rate and Time‑to‑Action beat model benchmarks
Measure: percentage of AI outputs executed without human rework (Action Rate) and Time‑to‑Action. Track these weekly and correlate to cash flow outcomes.
4) Treat exceptions as the product
Define exception types, owners, SLAs, and a shrinking target per sprint. Exception handling is where compliance and cost concentrate.
5) Weekly gold‑set audits are non‑negotiable
Run weekly evaluations (50–200 real cases) scored for accuracy, safety and compliance. Keep evidence: regulators and auditors will expect these records.
6) Role‑based copilots with access controls reduce risk
Separate copilots by function (sales, finance, claims) with explicit data access rules, approval thresholds and audit logs.
7) Prioritize high‑volume, predictable functions
Start with AP/AR, claims intake, procurement or first‑touch support. Unit economics are measurable and repeatable there.
8) Contract your data—don’t wait for perfection
Use one‑page data contracts that specify sources, freshness, acceptance thresholds and owners. Getting usable guarantees fast beats endless cleansing.
9) Policy design outranks prompting
Define what the system can do autonomously, what requires approval, and what to log. Automate enforcement of those policies.
10) Require a dirty‑data proof
Insist vendors run your last 60–90 days of real cases on their stack. If they refuse, they are refusing commercial accountability.
11) Assign a business owner and tie to the P&L
Name one accountable person for one measurable business metric. If someone can’t win or lose against a metric, ROI won’t appear.
Updated scorecard — add governance and legal checkpoints
- Action Rate (% outputs executed)
- Exception Rate and root causes
- Time‑to‑Action
- Unit Economics (cost per processed item; margin impact)
- Quality Evals (weekly gold‑set score)
- Risk & Compliance (DPIA complete, EU AI Act high‑risk status, audit log completeness)
- Drift Rate (monthly change in gold‑set accuracy)
- Data Contract (signed, fields, freshness, owner)
- Business Owner (named, with P&L tie)
Impact: who wins, who loses
Winners are teams that treat AI as an operations program: instrumented handoffs, weekly audits, and named business owners with legal sign‑off. Losers are teams that keep treating AI as a vendor selection exercise or as a tech experiment with no P&L owner. The immediate consequence in July 2026: faster procurement cycles for vendors that provide dirty‑data proofs and built‑in logging; stalled pilots where vendors won’t validate on customer data.
Reactions from the field
“We doubled realized savings after forcing the vendor to run our last 90 days of claims,” an operations VP at a 500‑employee insurer told me in March 2026. “The model was fine; the game changer was making exceptions measurable and owning them.”
In June 2026 a head of product at a mid‑market B2B SaaS company in Boston said: “When legal required a DPIA and logging before scaling, it felt like friction — until we saw fewer surprises in production. Compliance slowed deployment but raised the signal‑to‑noise in our metrics.”
Your rights and legal obligations
If your AI handles personal data, the law requires documented purpose limitation and a lawful basis for processing under the GDPR. The GDPR also requires a Data Protection Impact Assessment (DPIA) where processing is likely to result in high risk to individuals (Article 35). For automated decision‑making that produces legal or similarly significant effects, Article 22 and related guidance constrain how you may act without human involvement.
The EU AI Act (for systems classified as high‑risk) will require conformity assessments, technical documentation and post‑market monitoring — meaning operational controls and logs are not optional. In the U.S., the FTC continues to treat deceptive automation claims and inadequate oversight as enforcement priorities. State privacy laws (California CPRA, Virginia CDPA, Colorado CPA) impose notice and data‑subject rights that affect what data you can ingest and how you document use.
Actionable legal steps: perform a DPIA before scale, retain audit logs as required by sector rules (financial services often face 3–7 year retention obligations—check FINRA/SEC rules), and get written legal sign‑off on data contracts and retention policies. Consult qualified counsel for jurisdiction‑specific legal advice.
Do this in the next 7 days: updated, legally aware checklist
- Pick one workflow (target 100+ cases/week; 25–50 for small firms) tied to a specific P&L line.
- Define the exact action the AI must trigger (not “assist”).
- Create a 100‑case gold set from the last 60–90 days and score it with a legal/compliance rubric.
- Design the exception queue with owners, SLAs and a shrinking backlog target.
- Require the vendor to run a dirty‑data proof on your actual inputs before signing scaled contracts.
- Log every output, every decision, and retain logs per sector rules; start with a 1–3 year baseline and adjust per counsel.
- Have legal sign off on DPIA, data contract and retention plan prior to rollout.
- Report a one‑page scorecard to the CFO/board weekly: Action Rate, Unit Economics, Exception Rate, and Compliance flag.
What’s next — Q3–Q4 2026 watchlist
Expect procurement to require dirty‑data proofs and scorecard templates, and for boards to demand combined economic/compliance scorecards. Vendors that bake in audit trails, drift monitoring and on‑demand dirty‑data pilots will capture enterprise deals. For buyers: stop optimizing models in isolation; optimize decisions, handoffs and ownership. The law requires oversight; your competitive advantage will come from owning it.
How should I prove ROI to the board?
Deliver a one‑page scorecard for a single workflow showing Action Rate, Unit Economics and Exception Rate over a 6‑week run. Tie savings to a P&L line and name the accountable owner. Boards want business outcomes, not model perplexity.
Do I need a legal review before a pilot?
Yes. If the pilot touches personal data, customer outcomes or consumer marketing, get legal and privacy teams involved upfront. They will require a DPIA where applicable, retention rules for logs and clear escalation paths for adverse outcomes.
What if my vendor won’t run dirty data tests?
Treat that as a disqualifier. A vendor unwilling to validate on your real inputs is refusing commercial accountability. Insist on a contract clause or a pilot on real data, or find a partner who will.
Can small companies follow this playbook?
Yes. Scale everything down: one workflow, 25–50 cases/week, same scorecard discipline. Ownership, logging and weekly evaluations scale to small teams and produce compounding learnings.
Consult a qualified attorney for jurisdiction‑specific legal advice. This article explains operational and legal considerations; it is not legal advice.